Learn To Spot “DeepFakes”

Learn To Spot “DeepFakes”

LEARN TO SPOT “DEEPFAKES”

From: SANS Security Awareness

What Are Deepfakes?

The word “deepfake” is a combination of “deep learning” and “fake.” Deepfakes are falsified pictures, videos, or audio recordings. Sometimes the people in them are computer-generated, fake identities that look and sound like they could be real people. Sometimes the people are real, but their images and voices are manipulated into doing and saying things they didn’t do or say. For example, a deepfake video could be used to recreate a celebrity or politician saying something they never said. Using these very lifelike fakes, attackers can spin up an alternate reality where you can’t always trust your eyes and ears.

Some deepfakes have legitimate purposes, like movies bringing deceased actors back to life to recreate a famous character. But cyber attackers are starting to leverage the potential of deepfakes. They deploy them to fool your senses, so they can steal your money, harass people, manipulate voters or political views, or create fake news. In some cases, they have even created sham companies made up of deepfake employees. You must become even more careful of what you believe when reading news or social media in light of these attacks.

The FBI warns that in the future deepfakes will have “more severe and widespread impact due to the sophistication level of the synthetic media used.” Learn to spot the signs of a deepfake to protect yourself from these highly believable simulations. Each form of deepfake — still image, video, and audio — has its own set of flaws that can give it away.

Still Images

The deepfake you may see most often is the phony social media profile picture. The image below is an example of a deepfake from the website thispersondoesnotexist.com. Below the image are five different clues that this could be a deepfake. You will notice that these clues are not easy to spot and can be hard to identify:
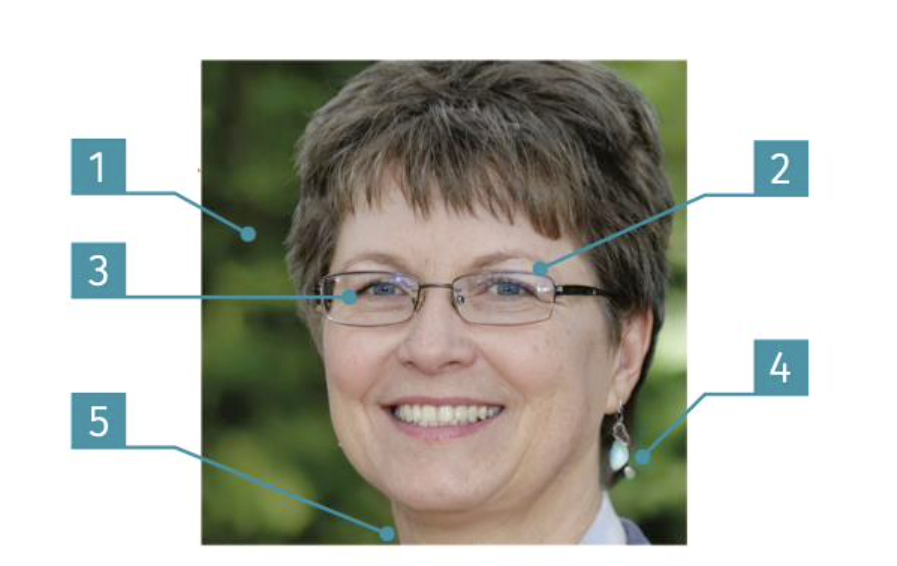
OUCH_March_2022_still_image.png

  1. Background: The background is often blurry or crooked, and may have inconsistent lighting such as pronounced shadows pointing in different directions.
  2. Glasses: Look closely at the connection between the frames and the arms near the temple. Deepfakes often have mismatching connections with slightly different sizes or shapes.
  3. Eyes: Deepfake photos currently used for fake profile pictures appear to have their eyes in the same spot in the frame, resulting in what some call the “deepfake stare.”
  4. Jewelry: Earrings may be amorphous or strangely attached. Necklaces may be embedded into the skin.
  5. Collars and shoulders: Shoulders may be misshapen or unmatching. Collars may be different on each side.

Video

Researchers at the Massachusetts Institute of Technology, MIT, developed a question list to help you figure out if a video is real, noting that deepfakes often can’t “fully represent the natural physics” of a scene or lighting.

  1. Cheeks and forehead: Does the skin appear too smooth or too wrinkly? Is the age of the skin similar to the age of the hair and eyes?
  2. Eyes and eyebrows: Do shadows appear in places that you would expect?
  3. Glasses: Is there any glare? Too much glare? Does the angle of the glare change when the person moves?
  4. Facial hair: Does the facial hair look real? Deepfakes might add or remove a mustache, sideburns, or beard.
  5. Facial moles: Does the mole look real?
  6. Blinking: Does the person blink enough or too much?
  7. Lip size and color: Do the size and color match the rest of the person’s face?

Audio/Voice

Researchers say technologies like spectrograms can show when voice recordings are fake. But most of us do not have the luxury of a voice analyzer when an attacker calls. Listen for a monotone delivery, odd pitch or emotion, and lack of background noise. Voice fakes can be hard to detect. If you receive an odd call from a legitimate organization, you can verify if the call is real by first hanging up then calling the organization back. Be sure to use a trusted phone number, such as a phone number you already have in your contact list, a phone number printed on a bill or statement from the organization, or the phone number on the organization’s official website.

Conclusion

Be aware that attackers are actively using deepfakes. They can make fake accounts on social media to connect with or create fake videos to influence public opinion. Some are even selling their services on the dark web so other attackers can do the same. We don’t expect you to become a deepfake expert, but if you arm yourself with the basics of identifying the fakes, you’ll be far better at defending yourself. If you suspect you have detected a deepfake, report it to the website or source that is hosting the content.
Cyber Security Dos & Don’ts for Remote Working

Cyber Security Dos & Don’ts for Remote Working

CYBER SECURITY DOS & DON’TS FOR REMOTE WORKING

During the past 2 years we’ve seen a huge shift to remote working due to the global health crisis, and despite some cyber security concerns, this may be a trend that will continue even once the pandemic passes. In fact, 74% of companies worldwide plan to encourage the trend of employees working remotely.

While this flexible working arrangement is definitely more convenient, it doesn’t come without its own set of risks — particularly in the realm of cyber security. In order to reduce the chances of your company becoming a target of a security risk or data breach due to people working from their home offices, it is important you reinforce some sound cybersecurity strategies.

Here, then, are some basic dos and don’ts to keep in mind if you are working from home, manage a remote team or full company of remote employees.

DON’T: Use public networks

Some public Wi-Fi networks need a password to log in, but that doesn’t automatically make them safe. Public networks are not secure, meaning other people can have easy access to it and there’s no firewall keeping you safe from malicious entities. One danger is you might end up logging on to a rogue network. This is essentially when a cybercriminal’s rogue hotspot pretends to be a public network, acting as a ‘middleman’ between you and the real network. This allows them to see all online traffic and even credentials you use.

DO: Ask employees to use a VPN

VPNs are a popular cybersecurity tool. While employees may use their own VPNs, some might skimp on it and go for the cheaper or even free ones. There are even fake VPNs out there that might end up stealing your data. Instead, opt for a business VPN, such as the Perimeter 81, which has a server designed for business users. They protect data and business security, not just the employees’. Confidential data and important files can be sent and accessed safely. Aside from security encryption, VPNs act as a proxy to the internet.

DON’T: Rely on just the home office router’s firewall

Home office routers already have default firewalls that keep intruders and third parties from infiltrating your personal gadgets. However, attackers have figured out how to hack them. Consider supplementing your home router firewall with a hardware firewall. It uses PCBs that are designed and manufactured using materials like solder mask, silk screen, and copper all on one board. The small board can accommodate elaborate security functions to ensure your network is safeguarded against external threats.

DO: Update your company’s software

Computer updates aren’t just there to add features and improve existing ones or to give you more speed. Software updates also patch security flaws. After all, cyber criminals are always coming up with new malware and trying to look for security lapses in your organizational IT infrastructure. So before you shrug off that software update notification, think twice as you might be putting your device and your business’s sensitive information at risk.

DON’T: Assume that your business is safe

This is the most important thing you should avoid. As previously mentioned, cybercriminals are always looking for ways to attack businesses and individuals. According to 2021 cybercrime predictions, there is a cyber attack every 11 seconds and it will cost the global economy at least $5.7 billion a year. Truth be told, the perfect security strategy doesn’t exist. However, having enough measures in place can significantly lower your chances of being targeted. It is also important for employees and employers, both, to have some basic level of cyber security training so that they understand what repercussions their actions can have.

DO: Learn about phishing attacks

Executives and cybersecurity professionals aren’t the only ones who need to know how to handle cyber attacks. Unfortunately, even the best VPNs and anti-virus software won’t be able to do anything if employees fall prey to phishing attacks. You can train them by conducting phishing simulation tests, which can help them recognize phishing attacks. On top of this, you can also consider holding internal training or providing them with high quality literature so they can educate themselves on the common cyber threats and attacks mechanisms.

First American State Bank offers a variety of personal banking and lending products to existing and new customers. We value personal banking relationships with our customers and strive to accommodate all your banking needs.

Spot & Stop Messaging Attacks

Spot & Stop Messaging Attacks

WHAT ARE MESSAGING (SMS) ATTACKS?

From: SANS Security Awareness – JANUARY 2022

Smishing (a portmanteau word combining SMS and phishing) are attacks that occur when cyber attackers use SMS, texting, or similar messaging technologies to trick you into taking an action you should not take. Perhaps they fool you into providing your credit card details, get you to call a phone number to get your banking information, or convince you to fill out an online survey to harvest your personal information. Just like in email phishing attacks, cyber criminals often play on your emotions to get you to act by creating a sense of urgency or curiosity, for example. However, what makes messaging attacks so dangerous is there is far less information and fewer clues in a text than there is in an email, making it much harder for you to detect that something is wrong.

A common scam is a message telling you that you won an iPhone, and you only need to click on a link and fill out a survey to claim it. In reality, there is no phone and the survey is designed to harvest your personal information. Another example would be a message stating that a package could not be delivered with a link to a website where you are asked to provide information needed to complete delivery, including your credit card details to cover “service charges.” In some cases, these sites may even ask you to install an unauthorized mobile app that infects and takes over your device.

Sometimes cyber criminals will even combine phone and messaging attacks. For example, you may get an urgent text message from your bank asking if you authorized an odd payment. The message asks you to reply YES or NO to confirm the payment. If you respond, the cybercriminal now knows you are willing to engage and will call you pretending to be the bank’s fraud department. They will then try to talk you out of your financial and credit card information, or even your bank account’s login and password.

SPOTTING AND STOPPING MESSAGING ATTACKS

Here are some questions to ask yourself to spot the most common clues of a messaging attack:

  • Does the message create a tremendous sense of urgency attempting to rush or pressure you into taking an action?
  • Is the message taking you to websites that ask for your personal information, credit card, passwords, or other sensitive information they should not have access to?
  • Does the message sound too good to be true? No, you did not really win a new iPhone for free.
  • Does the linked website or service force you to pay using non-standard methods such as Bitcoin, gift cards or Western Union transfers?
  • Does the message ask you for the multi-factor authentication code that was sent to your phone or generated by your banking app?
  • Does the message look like the equivalent of a “wrong number?” If so, do not respond to it or attempt to contact the sender; just delete it.

If you get a message from an official organization that alarms you, call the organization back directly. Don’t use the phone number included in the message, use a trusted phone number instead. For example, if you get a text message from your bank saying there is a problem with your account or credit card, get a trusted phone number on your bank’s website, a billing statement, or from the back of your bank or credit card. Also remember that most government agencies, such as tax or law enforcement agencies, will never contact you via text message, they will only contact you by old fashioned mail.

When it comes to messaging attacks, you are your own best defense.

Village Toy Drive 2021

Village Toy Drive 2021

VILLAGE TOY DRIVE 2021

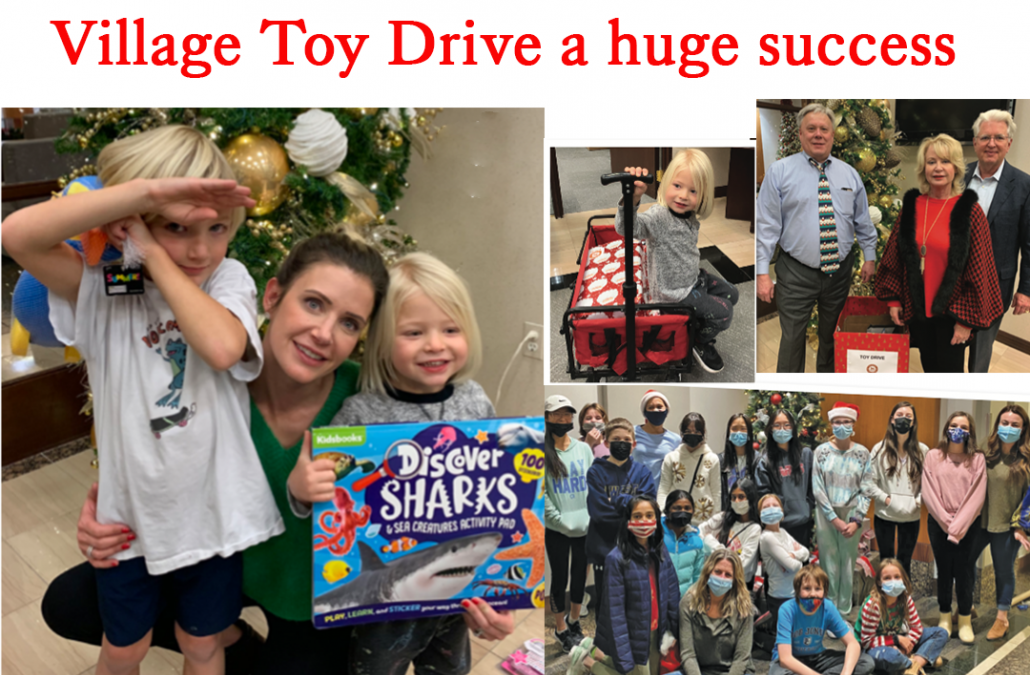
The Village Toy Drive was a huge success with just under 900 gifts donated and $6,000 raised that went towards buying gift cards for the teenagers. This 8th Annual event is presented by First American State Bank, Volunteers of America, Cherry Village Living and Gruber Commercial Real Estate, Inc. The final wrapping party was held on Thursday, December 17 at First American State Bank with Vice President, Michelle Gruber at the helm busily wrapping and responsible for coordinating this amazing toy drive. Every employee along with Volunteers of America staff, West Middle School student Council, friends of friends and even local radio personality Kim Monson of The Kim Monson Show was there to help with the final “wrap up” so that less fortunate families the Denver Metro area will have a glorious Christmas.

Toys are being delivered by Volunteers of America this week along with 1,500 Christmas baskets to families in need. There was a raffle drawing held for anyone whom donated cash and or gift items and the lucky winners were Jim Cull, the recipient of two club level tickets for Broncos vs Cincinnati Bengals game on 12/19/2021 with a valet pass and Charlie McNeil won the bottle of Elway’s Reserve Cabernet Sauvignon wine signed by the man himself, John Elway.

Click Here To Download Article

Top Cybersecurity Tips For Vacations

Top Cybersecurity Tips For Vacations

TOP CYBERSECURITY TIPS FOR VACATIONS

Overview

As the holiday season approaches, millions of people will be traveling. If you are among the many, here are some tips to help keep you cyber-savvy and safe.

  • Mobile Devices: Bring as few devices as you can. The fewer devices you bring while traveling, the fewer devices that can be lost or stolen. In fact, did you know that you are far more likely to lose a mobile device than have it stolen? Whenever leaving a hotel room, restaurant, taxi cab, train, or airplane, do a quick device check and make sure you have all of your devices. Don’t forget to have friends or family traveling with you to double-check for their devices too, like children who may leave a device behind on a seat or in a restaurant.

As for the devices you choose to bring, make sure you update them so they are running the latest operating system and apps. Keep the screen lock enabled. If possible, ensure you have some way to remotely track your devices if they are lost. In addition, you may want the option to remotely wipe the device. That way if a device is lost or stolen, you can remotely track and/or wipe all your sensitive data and accounts from the device. Finally, do a backup of any devices you take with you, so if one is lost or stolen, you can easily recover your data.

  • Wi-Fi Connections: When traveling, you may need to connect to a public Wi-Fi network. Keep in mind you often have no idea who configured that Wi-Fi network, who is monitoring it or how, and who else is connected to it. Instead of connecting to a public Wi-Fi network, whenever possible connect to and use the personal hotspot feature of your smartphone. This way you know you have a trusted Wi-Fi connection. If that is not possible and you need to connect to a public Wi-Fi network (such as at an airport, hotel, or cafe), use a Virtual Private Network, often called a VPN. This is the software you install on your laptop or mobile devices to help protect and anonymize your Wi-Fi connection. Some VPN solutions include settings to automatically enable the VPN when connecting to non-trusted Wi-Fi networks.
  • Public Computers: Avoid using public computers, such as those in hotel lobbies or at coffee shops, to log into any accounts or access sensitive information. You don’t know who used that computer before you, and they may have infected it accidentally or deliberately with malware, such as a keystroke logger. Stick to devices you control and trust.
  • Social Media: We love to update others about our travels and adventures through social media, but we don’t always know who every friend or viewer is online. Avoid oversharing while on vacation as much as possible and consider waiting to share your trip until you’re home. Additionally, don’t post pictures of boarding passes, driver’s licenses, or passports as this can lead to identity theft.
  • Work: If you will be working while on vacation (we hope not!), make sure you check what your work travel policies are ahead of time, including what devices or data you can bring with you and how to remotely connect to work systems safely.

Vacation should be a time for relaxing, exploring, and having fun. These simple top cybersecurity tips for vacations will help ensure you do so safely and securely.